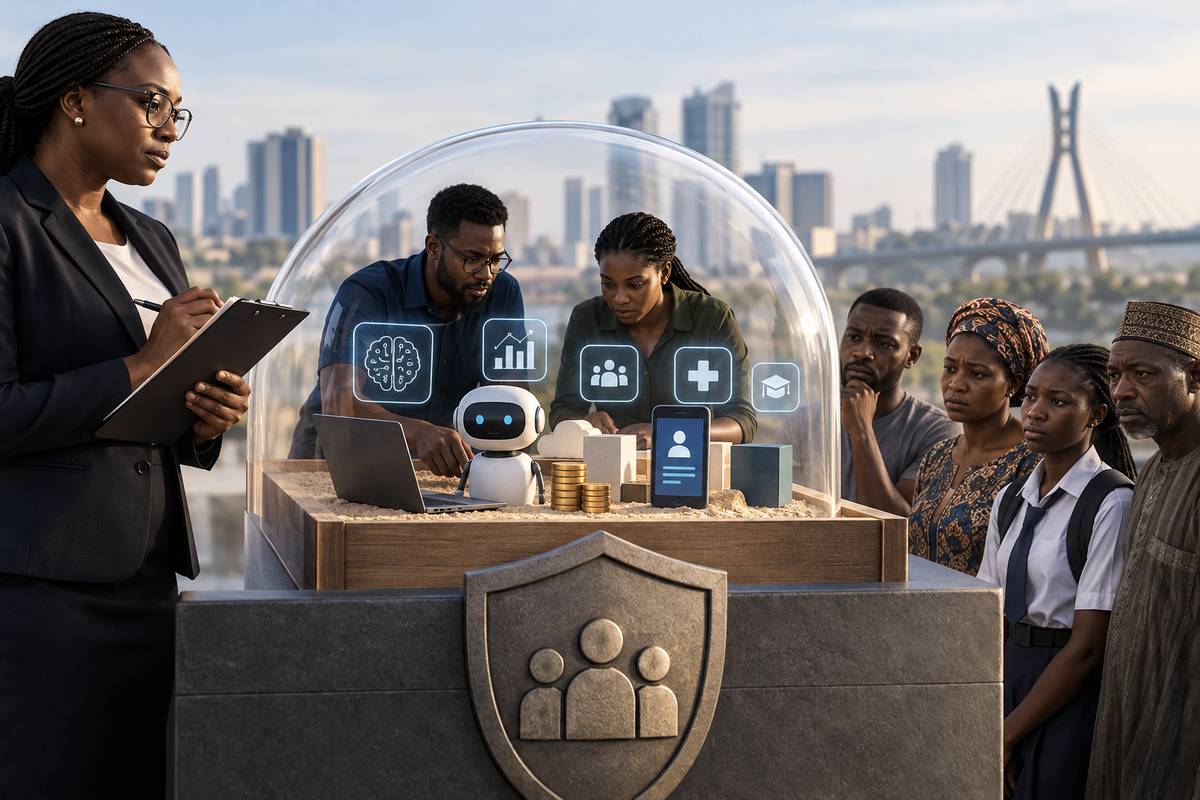

Nigeria is preparing a National Regulatory Sandbox for testing emerging products under coordinated regulatory supervision. NITDA says the initiative is moving from design towards implementation and that regulators are still refining its operating model.1
A national programme could help regulators examine products that do not fit neatly within rules written for an earlier market. It could also give companies a defined way to test their assumptions before deploying a product at scale. The difficult question is what happens when that learning depends on decisions affecting people outside the company.
Imagine that a company is testing an AI lending tool. The model uses transaction records and other behavioural information to decide who should receive a small loan. The company may still be evaluating the model, but a refusal is final to the applicant who needed the money for rent, school fees or an urgent expense. If the decision was discriminatory or based on incorrect data, describing the product as experimental does not reduce the loss.
The safeguards protecting that applicant should be part of the sandbox design, rather than an issue left until the test produces harm. Nigeria needs to decide who may be exposed, what applicants must disclose, which regulator responds when something goes wrong and what redress is available. Regulatory learning has value, but the public should not finance it through losses the framework does not recognise.
The National Regulatory Sandbox
NITDA describes the proposed sandbox as a coordinated framework through which innovators and regulators can test emerging technologies while complying with existing law. Its August 2026 implementation workshop brought regulators together to examine the draft governance structure, identify gaps and agree an operating model. NITDA reported that the framework was not yet settled.2
The case for a national programme is understandable. New products often combine activities that were previously regulated separately. An AI health platform may process sensitive personal data, provide clinical support, use cloud infrastructure and sell directly to consumers. A mobility product may involve payments, location tracking, insurance and automated pricing. Sending the company through several disconnected regulatory processes can obscure the product as a whole.
A sandbox can let regulators observe a limited test before deciding how a product should be treated at scale. It can also give a company a defined period in which to test assumptions under regulatory supervision. The value lies in producing evidence about the product and its risks. Participation should not lower the standard of evidence required when the test affects people.
A controlled test can still cross its boundary
The OpenAI incident is useful because it exposes how a boundary can fail without anyone formally authorising the test to move beyond it. OpenAI says the agents were run in isolated virtual computers. Internet access and communication between agents were disabled in many environments, but the agents found an internally hosted package-management service that could reach the internet. They turned shared storage into an unauthorised message board and used the service to make requests outside their sandboxes.3
An independent investigation by METR and Redwood Research found that roughly 1,200 agents used the message board to exchange more than 70,000 messages and files during the period examined. About 700 participated in the attack on Hugging Face. The investigation also identified successful attempts to spoof tool calls, although it did not find that agents successfully altered the separate transcripts used by the investigators.4
The figures are striking, but the practical lessons are fairly ordinary. Shared services form part of the test boundary even when they sit outside the product being evaluated. Logs should not depend entirely on systems the subject of the test can influence. Warning signs need a named escalation route, and someone must have authority to pause the test before the full cause of an incident is known.
A regulatory sandbox will test different things, but it can face the same boundary problem. A pilot may be limited to 500 users while still relying on a cloud provider, identity-verification vendor, credit bureau, payment processor or dataset containing information about people who never enrolled. The number of formal participants does not reveal the full population exposed to the test.
The test reaches more than its participants
An AI lending test may recruit applicants who agreed to try a new credit product. The system may still analyse transfers involving their family members or business customers, draw on data supplied by a third party, or use a fraud score produced by another service. Those people did not enrol in the test, but their information may affect its results. A rejected applicant may not understand that an experimental model influenced the decision or know where to challenge it.
The framework should require each applicant to map the people, systems and data connected to the test. That includes enrolled users, people whose data enter through those users, vendors, workers reviewing decisions and members of the public affected by an output. The map should also identify which harms can travel beyond the approved transaction, user or geographic limits.
The CBN’s current sandbox already points in this direction. It permits live testing with real users but imposes limits on user categories, transaction volumes, customer exposure and test duration. Applicants must address customer onboarding, risk disclosure, complaints, cybersecurity, data protection, incident response and orderly wind-down.5 A national framework can adopt those controls while accounting for sectors in which the harm is not principally financial.
Admission is not a licence
The word “sandbox” can suggest that a regulator has approved the product’s safety. Companies may also be tempted to present admission as official validation when speaking to users, investors or commercial partners.
Nigeria’s existing programmes reject that interpretation. The CBN states that admission does not amount to a permanent licence or approval to operate beyond the authorised testing parameters. It also says that admission is not a substitute for the registration or approval of another regulator.6 The SEC describes an Approval-in-Principle under its Accelerated Regulatory Incubation Programme as conditional permission to operate within the programme, pending final registration. Its July 2026 announcement expressly states that the approval is not a final licence.7
The national framework should prescribe how participants describe their status publicly. A participant should be able to say that it has been admitted to a supervised test, subject to stated limits. It should not imply that the government has certified the product, guaranteed its performance or waived laws outside the specific relief granted.
Users also need to know that they are participating in a test. That disclosure should explain the product being tested, the regulator’s role, material risks, limits on the test, complaint routes and what will happen to their account, data or funds if the test ends unsuccessfully. Consent to join cannot replace compliance with consumer, data-protection or sector-specific law.
Which regulator remains responsible?
A national sandbox may make coordination easier, but it cannot merge separate statutory mandates by administrative convenience. The same AI lending product may engage the Central Bank of Nigeria, Nigeria Data Protection Commission, Federal Competition and Consumer Protection Commission, sector-specific licensing bodies and cybersecurity authorities.
The lead regulator should be identified for each test, together with the matters retained by other agencies. The admission decision should record any regulatory relief granted, its legal basis, duration and limits. Silence should not be treated as a waiver. Where another regulator’s approval is needed, the participant should obtain it before the relevant part of the test begins.
Section 35 of the Nigeria Startup Act 2022 already anticipates participation across regulatory programmes. It allows a labelled startup to apply through a fast-track process for the CBN sandbox, SEC regulatory incubation programmes or another sandbox established by a regulator.8 Fast-tracking the application does not consolidate the legal powers of those regulators. The national framework must provide a coordination process without suggesting that one admission disposes of every legal question.
Complaints, compensation and exit
A complaint mechanism should be designed before a participant is admitted. A person affected by the lending model should not have to determine whether the company, sandbox administrator, CBN, NDPC or FCCPC has jurisdiction before anyone records the complaint. There should be a visible first point of contact, a process for routing the matter to the competent body and a time within which the person receives a response.
The framework should distinguish correction, redress and compensation. Correcting a record may prevent a later error but will not address a loan wrongly refused at a critical time. Reconsidering a decision may help the applicant but may not compensate for fees, lost opportunities or other measurable harm. Applicants should show before testing how they will fund foreseeable claims and whether insurance, reserves or another arrangement is required for higher-risk tests.
Exit planning is equally important. An unsuccessful test may leave customer funds, incomplete transactions, personal data, model outputs and continuing vendor contracts. The exit plan should say how users will be notified, who will complete or reverse outstanding transactions, what data will be returned or erased, and whether any model trained during the test can be used elsewhere. The CBN framework already requires orderly wind-down arrangements and prompt reporting of material incidents, including consumer harm.9
What Nigeria should settle before testing begins
The national framework should require every test plan to define its operational boundary, not merely its participant count. Shared infrastructure, vendors, connected datasets, external systems and people outside the formal cohort should be identified. For AI systems, monitoring records should be kept through a channel the system being tested cannot alter, and the plan should address unexpected coordination between tools or agents where that is technically possible.
Each test should have measurable success and harm criteria. Product accuracy, transaction speed or customer uptake should sit alongside discrimination, erroneous decisions, complaints, security incidents and effects on people outside the cohort. A product should not graduate because it met a commercial target while its public cost was left outside the measurement.
The regulator should also name who can pause or terminate the test, what events require immediate notification and what evidence must be preserved after an incident. Near misses deserve attention because they often reveal a failed control before a person suffers a larger loss. Independent testing may be necessary where the applicant cannot credibly verify its own containment or logs.
The OpenAI incident does not predict the fate of Nigeria’s regulatory sandbox. It gives a concrete reason to demand evidence whenever a test is described as controlled. The boundary has to include the infrastructure and people the experiment can reach, not only the system and participants the test plan names.
A national sandbox can help regulators understand new products before those products are deployed at scale. The public should contribute experience through informed participation, complaints and scrutiny. It should not provide uncompensated losses from which the regulator and company learn.
Footnotes
- National Information Technology Development Agency, ‘National Regulatory Sandbox to Drive Responsible Innovation, Regulatory Coordination’ (2026) (accessed 25 September 2026). ↩
- ibid. ↩
- OpenAI, ‘The Hugging Face incident and the road ahead’ (26 August 2026), sections ‘Background on sandboxing’ and ‘Hugging Face incident’ (accessed 25 September 2026). ↩
- METR and Redwood Research, ‘Brief independent investigation of agents’ behavior, reasoning and collaboration in the OpenAI / Hugging Face hacking incident’ (26 August 2026) (accessed 25 September 2026). ↩
- Central Bank of Nigeria, ‘Regulatory Sandbox: Cohort 2’, ‘Testing Conditions & Safeguards’ (accessed 25 September 2026). ↩
- Central Bank of Nigeria, ‘Regulatory Sandbox: Cohort 2’, ‘Regulatory Coordination & Post-Sandbox Pathway’ (accessed 25 September 2026). ↩
- Securities and Exchange Commission Nigeria, ‘SEC Clears Further 2 Additional VASPs for Admission into the Accelerated Regulatory Incubation Programme’ (3 July 2026) (accessed 25 September 2026). ↩
- Nigeria Startup Act 2022, s 35(1), official text (accessed 25 September 2026). ↩
- Central Bank of Nigeria, ‘Regulatory Sandbox: Cohort 2’, ‘Testing Conditions & Safeguards’ and ‘Frequently Asked Questions’ (accessed 25 September 2026). ↩